ISO 27001 certification checklist
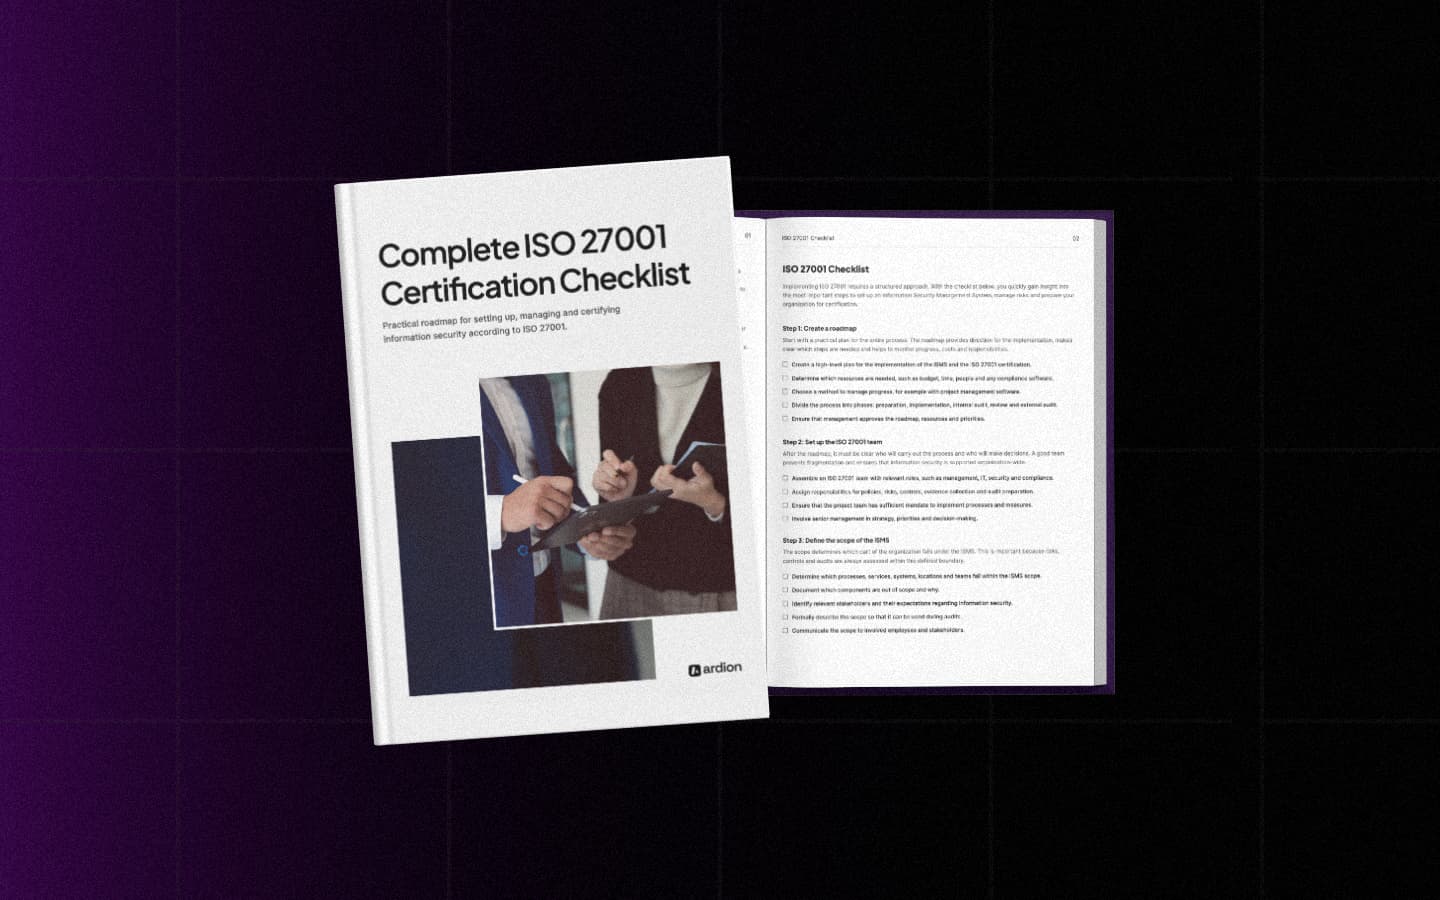
A practical roadmap for setting up, managing and improving an Information Security Management System on the way to ISO 27001 certification.
Download for free
What is inside
Preparing for ISO 27001 certification can feel complex. The process involves many separate components, including scope definition, risk assessment, policy development, control implementation, documentation, internal audits and management review. This practical guide breaks the ISO 27001 implementation process down into clear and manageable steps.
- Structure your ISO 27001 implementation with a practical roadmap.
- Define the scope of your ISMS and identify relevant stakeholders.
- Map information assets and assess information security risks.
- Create a risk register, treatment plan and Statement of Applicability.
- Develop policies, procedures and controls that support your ISMS.
- Prepare for employee training, evidence collection, internal audits and management review.
- Understand the key steps toward external ISO 27001 certification and continuous improvement.